The email comes from your client. You know the address. You know the conversation. The request makes sense in the context of everything that has gone before. So, you process the payment.
Except your client never sent the email.
Someone else has been sitting inside the account, reading the correspondence, and waiting for money to move. They know who is involved, what is being discussed, and, potentially, when money is about to move. By the time the fraudulent instruction lands in your inbox, the fraudster may already know the relationship better than you realise.
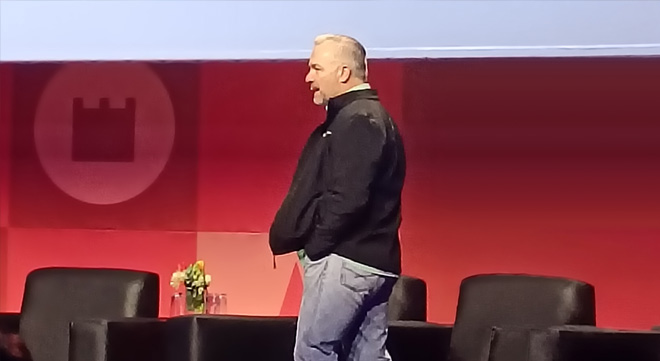
That is business email compromise (BEC), the focus of Kevin Hogan’s (pictured) presentation at the Morningstar Investment Conference in Cape Town on 10 September 2026. Hogan, head of fraud risk at Investec Bank, described it as the “biggest corporate fraud in the world”.
It starts with a simple message
There is a reason fraudsters aren’t trying to breach a bank’s firewall anymore. They don’t have to. They found an easier way in: bridging the human firewall.
Phishing, Hogan said, is how fraudsters get into email accounts in 99% of cases. It involves impersonating someone the recipient is likely to trust, with the aim of getting them to reveal information, click a link, or take an action that gives the fraudster access. It can begin with an email, an SMS, or even a telephone call.
A common example is an SMS saying that an outstanding package is waiting for delivery and asking the recipient to pay a delivery fee. The link takes the recipient to a page asking for credit card details. They’ve got you.
Another is an email purporting to come from your bank. The message says a payment has been unsuccessful and includes an attachment for confirmation. Even the contact numbers in the email can be genuine bank contact numbers.
The fraudster is banking on one thing: you won’t call. Why wait in a long calling queue if you can sort it out yourself by opening the attachment?
The attachment directs the recipient to a page made to look like the bank’s online banking login. Once the username and password are entered, the details are passed through to the fraudster’s access to the genuine banking site. An OTP follows. The victim assumes it is simply part of the normal login process. By approving it, however, the victim has given the fraudster access to the account.
A compromised email account can be used without its owner immediately noticing. A fraudster can create rules that search for messages containing words such as “invoice” and divert those emails away from the legitimate recipient.
A genuine invoice can then be intercepted, and its banking details changed before it reaches the person who is supposed to pay.
Even a PDF is not beyond tampering. Banking details on an invoice can be altered, so the fact that a document looks like one a client or supplier normally sends is not enough.
Email is convenient. That is the problem.
Email is probably the easiest way for a practice to communicate with clients. It is also one of the easiest channels for a fraudster to exploit.
Hogan’s advice was to move sensitive communication off ordinary email where possible. For smaller practices, he suggested WhatsApp Business as a relatively inexpensive way of exchanging things such as KYC documents and banking details. He also pointed to the encryption offered by WhatsApp, while his presentation mentioned secure-chat solutions for practices looking for a more formal encrypted channel.
That means changing some familiar habits. Email is convenient precisely because everything can be sent, received, and stored in one place. But that convenience can come at a cost when the account itself has been compromised.
As Hogan put it: “One of the key elements to good cyber security is you’re going to have to accept the fact that you’re going to need to give up some convenience.”
Don’t skimp on the password
When it comes to passwords, Hogan’s advice was simple: make them long, make them unique, and stop making life easy for fraudsters.
Some familiar bad habits remain: using the same username and password for different accounts, choosing short passwords, and continuing to use old passwords. He said he had personally seen a password of eight characters or fewer cracked in under 10 seconds.
His recommendation is at least 15 characters for every account, with a different password for each one. Passphrases are another option – a longer combination of words or even a sentence. Length matters.
Remembering a different 15-character password for every account is not realistic, which is where a password manager comes in. It generates and stores unique passwords, leaving the user with one master password to remember. Investec provides password managers to its staff, and businesses can buy corporate licences.
A strong password should not be the only barrier protecting a business email account.
Hogan recommended making two-factor authentication (2FA) compulsory. A password is only the first step; the user must then provide another form of authentication, such as an authenticator code or approval, a security key or, depending on the service, a code sent to a phone.
Microsoft 365, Google Workspace, and other major business and cloud services offer multi-factor authentication. The recommendation is to make it compulsory rather than leave it to individual employees to switch on.
Hogan also advised against single sign-on (SSO), which allows users to access multiple services using one set of login credentials – for example, signing in to a service using a Google or Facebook account. He argued that this can reinforce the very password habits he was warning against.
Technology is only part of the answer. Practices also need to educate employees and clients about phishing, smishing (phishing conducted via SMS or text message), and BEC. Someone still has to recognise the suspicious message before clicking.
Insurance cover is another area that warrants attention. Hogan said the fidelity fund does not cover cyber cover, while fidelity insurance covers staff fraud. His advice was to revisit commercial policies and check whether they include cyber-liability insurance.
Don’t trust the instruction. Pick up the phone.
One of the best controls against payment fraud is also one of the simplest: pick up the phone and verify the instruction.
The FAIS General Code of Conduct requires an FSP to have and effectively employ resources, procedures, and appropriate technological systems that can reasonably be expected to eliminate, as far as reasonably possible, the risk of clients and others suffering financial loss through theft, fraud, negligence, and other dishonest or culpable acts.
Payment controls need to be designed around the risk, with bank details independently authenticated before money moves.
At Investec, a request to make a payment or change banking details is not accepted simply because it arrives from a familiar email address. The process is to call the client using the number held on record and authenticate the instruction over a recorded line.
The same principle applies when the request involves a supplier. If new banking details are provided, the supplier is contacted directly to confirm them. The email containing the new account number is not used to verify the change.
That extra step is built into Investec’s approach to client communication. The bank does not use an automated call-centre system where clients select options and wait to be routed to the appropriate department. Instead, clients speak to a real person from the outset.
Hogan said Investec had not experienced any such issues since COVID; the last incident he recalled was around 2019 and resulted from an operational failure. The controls were already in place. The problem was that the process was not followed.
Even the best procedure is of little use if someone decides to bypass it because they are in a hurry.
“If this happens to you and you’ve got the protocols in place, it’s going to be because someone on Friday afternoon at 3 o’clock didn’t follow the process because they wanted to go home, and you’re going to lose R5 million and sink your ship.”
When the FSP is left holding the can
What happens when the fraud succeeds, and the FSP is left holding the can? South African case law shows that liability depends on the circumstances surrounding the payment and the precautions available to prevent the loss.
In Fourie v Van der Spuy and De Jongh Inc. and Others, a client sought to recover R1.744m after money held in an attorney’s trust account was paid out incorrectly. The High Court in Pretoria found that the attorney had failed to exercise the skill, knowledge, and diligence expected of a practising attorney. She had continued transacting by email despite knowing that fraud was prevalent, without taking measures to protect herself or her client. The fact that fraud had occurred was no defence to her obligation to account, and the respondents were ordered to pay R1 744 599.45.
Edward Nathan Sonnenberg Inc v Hawarden [2024] ZASCA 90 reached a different outcome.
Judith Hawarden was buying a property for R6m. After a cybercriminal gained access to her email account, an ENS email containing its legitimate banking details was intercepted and altered. Hawarden ultimately transferred the R5.5m balance into the fraudster’s FNB account, believing she was paying ENS. She was at her bank at the time and had assistance from a Standard Bank employee, but she did not contact ENS to verify the banking details before making the transfer. She had, however, previously verified the seller’s agent’s banking details by telephone and had been warned about BEC.
The Gauteng High Court initially found ENS liable for the R5.5m loss. In June 2024, the Supreme Court of Appeal (SCA) overturned that judgment and dismissed Hawarden’s claim.
The SCA found that Hawarden had reasonable means to protect herself: she could have asked the ENS employees she had spoken to, or her bank, to verify the account details. The Court held that she had ample means to avoid the risk and that there was no reason to shift responsibility for the loss to ENS. It also rejected a general legal duty on creditors to protect debtors against the possibility of their accounts being hacked, citing the danger of indeterminate liability.
In Fourie, the attorney was held liable after failing to take reasonable precautions when dealing with trust money. In Hawarden, the claim against the conveyancers failed because the claimant had reasonable opportunities to protect herself against the risk.
Hogan said the banking regulator’s current stance is that where the bank has not materially contributed to the fraud, it generally bears no liability. The focus then turns to whether the customer bypassed security measures provided for the payment, with these questions being tested through Ombud adjudications.
Read: How scammers turn your trust against you
For FSPs, Hogan’s advice is to make bank-detail verification a non-negotiable part of the payment process. The potential consequences of a failure can be measured in millions.
“Can you take a R5m hit and still be in business tomorrow? Can you take a R10m hit?”